Key Notes
- About 618,000 booking records were accessed through an external provider, while airBaltic’s own systems were unaffected.
- Around 11,800 affected reservations include upcoming flights, with free airport check-in available.
- Payment and travel-document data were excluded, but passengers should watch for fraudulent refund messages.
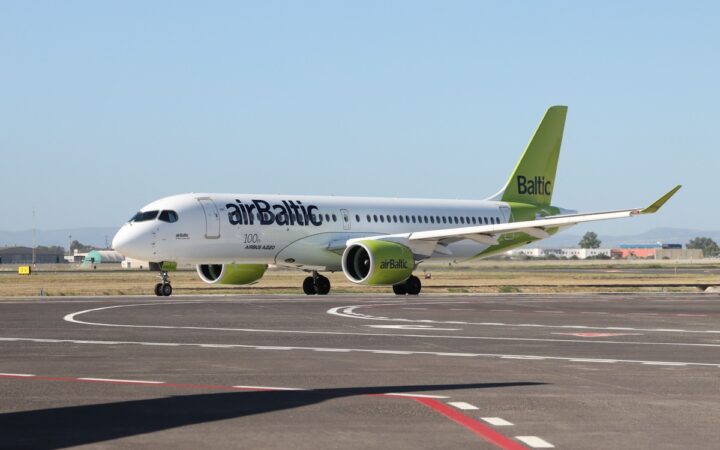
airBaltic has disclosed a data breach affecting approximately 618,000 booking records after unauthorized access to an external IT provider’s systems. The airline says about 11,800 affected reservations include upcoming flights, prompting it to disable online booking management and check-in for those bookings.
The carrier, based in Riga, said in its security notice that its own IT systems were unaffected. Flights are operating as scheduled, and passengers can still travel as planned.
Which Booking Data Was Accessed?
The incident concerns reservation records belonging to passengers who checked in online between July 18 and November 12, 2026. The information accessed includes names, booking references and flight details. airBaltic said payment information, travel-document details and other sensitive data were not involved.
The 618,000 figure refers to booking records, rather than a confirmed count of individual travelers. The investigation is continuing, and the airline cautioned that the number of affected upcoming reservations could change.
Free Airport Check-In for Affected Passengers
Online access has been restricted as a precaution against unauthorized changes to active bookings. Affected passengers can check in at the airport without a fee. As Latvian public broadcaster LSM reported, booking management and online check-in remain available as usual for passengers outside the affected online check-in group.
For travelers with an affected reservation, the practical change is where check-in takes place. If an online service is unavailable, contact the airline through its official website or app to confirm the arrangements for the booking.
Watch for Messages Offering Refunds
airBaltic says it has found no indication of misuse so far. It nevertheless warned that the exposed details could help scammers impersonate the airline or another travel provider, particularly in unexpected emails, texts or calls offering flight compensation or refunds.
A message containing genuine flight details is not, by itself, proof that the sender is legitimate. Open the airline’s website or app independently rather than following an unexpected payment or refund link.
We previously covered Singapore Airlines’ disclosure of booking-data exposure at Amadeus. airBaltic’s notice does not name its external provider, so a connection between the incidents has not been established.
Disclaimer: TravelCapybara is an independent media brand owned and operated by NuvexMedia LLC, publishing travel news, destination guides, research, and insights. NuvexMedia LLC may invest in or collaborate with companies across the travel, hospitality, technology, and digital media sectors. These relationships do not influence TravelCapybara’s editorial coverage. While we strive for accuracy, travel requirements, prices, schedules, availability, and local conditions may change without notice. Readers should independently verify information before making travel or purchasing decisions. This content is for informational purposes only and does not constitute professional advice. © 2026 NuvexMedia LLC. All rights reserved.